You send $50 to a friend. Simple, right? But if your wallet lives on Shard A and their wallet lives on Shard B, that simple transfer becomes a logistical nightmare. This is the core problem of Cross-Shard Communication. It’s the plumbing that allows partitioned blockchain networks to function as a single, coherent system rather than isolated islands. Without it, sharding-the primary method for scaling blockchains-falls apart because users can’t move value or data between shards without breaking security guarantees.
Why Shards Need to Talk
Sharding splits a blockchain into smaller, parallel chains called shards. Each shard processes its own subset of transactions, which boosts throughput significantly. But this isolation creates friction. If you want to swap tokens where one side is on Shard 1 and the other on Shard 2, those two shards must coordinate. They don’t share a common history or state by default. So, how do they agree that a transaction happened? That’s where cross-shard communication protocols step in. They provide the rules and cryptographic proofs needed to verify actions across boundaries.
Think of it like sending an email between two companies with different internal servers. The message has to leave Company A, travel through the internet (the public layer), and arrive at Company B, who then verifies it’s legitimate before updating their records. In blockchain, this "verification" isn't just about trust; it's about mathematical certainty.
The Mechanics: Receipts and Proofs
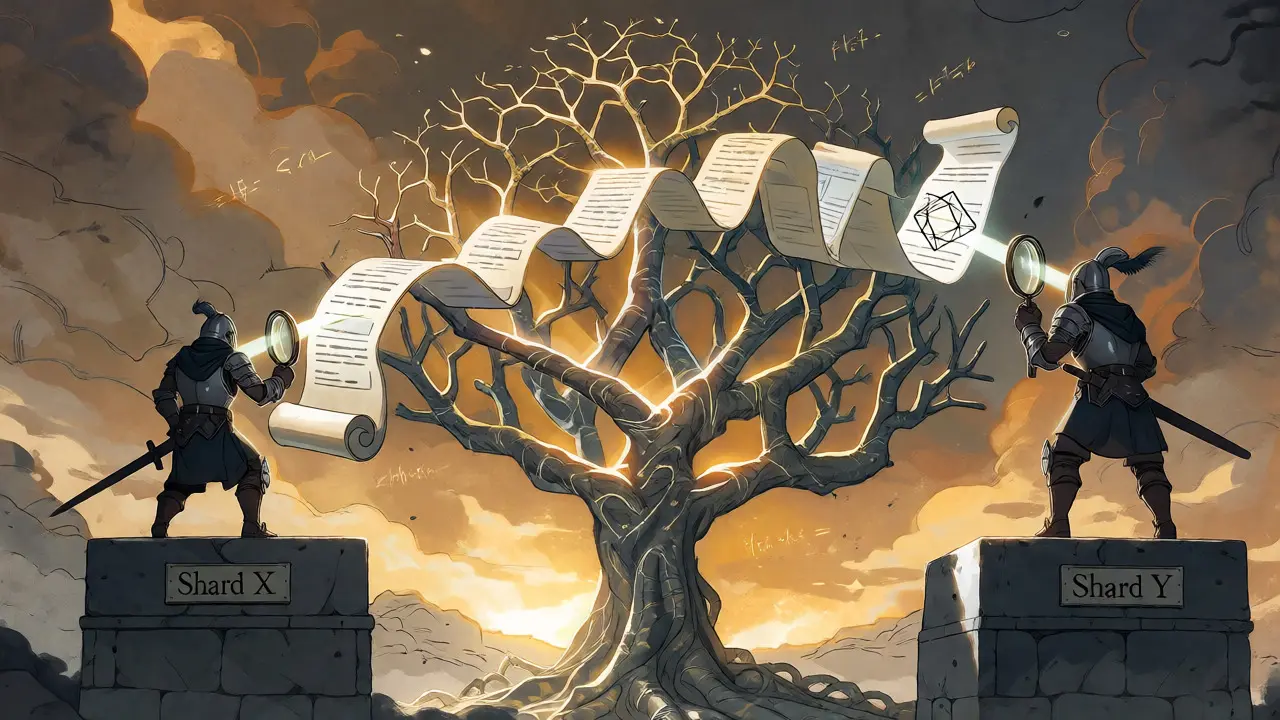
Ethereum’s approach to sharding relies heavily on receipts. When a transaction occurs on a source shard, it doesn’t just disappear. It generates a receipt-a compact record containing essential details like the sender, recipient, amount, and a unique identifier. This receipt is stored in the shard’s local state but is also made available to the destination shard via a mechanism often involving Merkle trees.
Here’s the step-by-step flow:
- Initiation: User A sends funds from Shard X. The transaction deducts coins from A’s balance on Shard X.
- Receipt Generation: Shard X creates a receipt proving this deduction occurred. Crucially, this receipt includes a Merkle proof linking it to Shard X’s latest state root.
- Transmission: This receipt is sent to Shard Y (where User B resides). This can happen via a relay contract or a dedicated messaging layer.
- Verification: Shard Y checks the Merkle proof against its knowledge of Shard X’s state roots. If the proof holds, Shard Y credits User B.
This process ensures that Shard Y doesn’t need to re-execute every transaction from Shard X. It only needs to verify the specific piece of evidence provided. This keeps the computational load low, preserving the scalability benefits of sharding.
Security Models: Fraud vs. Validity Proofs
How do we know the receipt isn’t fake? Two main security models handle this: fraud proofs and validity proofs.
| Feature | Fraud Proofs | Validity Proofs (zk-SNARKs) |
|---|---|---|
| Core Principle | Assume valid until challenged | Prove valid upfront |
| Cost | Low for honest actors, high for challengers | High computation cost to generate proof |
| Latency | Higher due to challenge period | Lower once proof is verified |
| Complexity | Simpler implementation initially | Mathematically complex |
Fraud proofs work on the assumption that most transactions are correct. If a malicious actor tries to submit a bogus receipt, anyone watching can spot the error and submit a proof showing the mistake. This triggers a penalty for the bad actor. However, this requires a waiting period for challenges, adding latency.
Conversely, validity proofs, such as zk-SNARKs, require the sender to generate a cryptographic proof that the transaction was executed correctly according to the rules. The receiving shard simply verifies this proof. No waiting periods, no assumptions-just math. While generating these proofs is computationally expensive, verification is fast. This model is increasingly favored in Layer 2 solutions and advanced sharding designs like ZK-rollups.
Handling State Consistency and Atomicity
The hardest part of cross-shard communication isn’t moving data; it’s maintaining consistency. What happens if Shard X says "I sent the money," but Shard Y crashes before crediting it? Or worse, what if Shard X rolls back the transaction after Shard Y already spent the funds?
To solve this, networks use atomic cross-shard composability. This means a multi-shard transaction either completes entirely or fails completely. There’s no half-way state. Achieving this requires sophisticated coordination. Some protocols use a two-phase commit style approach: first, lock the assets on the source shard; second, execute the action on the destination shard; third, finalize both sides. If any step fails, the entire operation reverts.
Dynamic state sharding adds another layer of complexity. Validators aren’t permanently assigned to one shard. They rotate periodically to prevent collusion attacks. This means the set of nodes verifying a cross-shard message changes over time. Protocols must ensure that even during validator rotations, the historical state roots remain accessible and verifiable so that old receipts can still be validated by new validators.
Real-World Implementations
Ethereum 2.0 remains the most prominent example of sharding in development. Its roadmap focuses on data availability sampling and beacon chain coordination to manage cross-shard messages efficiently. By separating consensus from execution, Ethereum aims to allow shards to operate independently while relying on the beacon chain for global synchronization.
Other projects take different angles. Shardeum, for instance, emphasizes linear scalability through dynamic state sharding. It attempts to achieve atomic cross-shard operations by using a novel consensus mechanism that coordinates transaction ordering across shards more tightly than traditional asynchronous methods. This reduces the window for inconsistencies and simplifies developer experience, making dApps feel like they’re running on a single chain.
These implementations highlight a key trade-off: speed versus simplicity. Asynchronous systems are faster but harder to reason about. Synchronous systems are easier to build but may bottleneck under high load. Most modern architectures aim for a hybrid, using async messaging for bulk transfers and sync mechanisms for critical atomic swaps.
Challenges and Future Directions
Despite progress, cross-shard communication faces hurdles. Latency remains a concern. Every hop between shards adds time. For high-frequency trading or gaming applications, even milliseconds matter. Developers are exploring lighter-weight proof systems and optimized networking layers to reduce this overhead.
Another issue is user experience. Currently, bridging assets between shards can feel clunky compared to moving funds within a single chain. Wallets need to track multiple shard states, and UIs must clearly indicate when a transaction is pending cross-shard confirmation. Improving this abstraction is crucial for mainstream adoption.
Looking ahead, research focuses on reducing the size of proofs and speeding up verification. Innovations in zero-knowledge cryptography continue to push the boundaries of what’s possible, allowing for more complex logic to be proven off-chain and verified on-chain with minimal gas costs. As these technologies mature, cross-shard communication will likely become invisible to end-users, functioning seamlessly in the background.
What is the difference between network sharding and state sharding?
Network sharding divides nodes into groups to improve communication efficiency, ensuring messages propagate quickly within a group. State sharding, however, partitions the actual ledger data (balances, smart contracts) across these groups. Cross-shard communication primarily deals with state sharding challenges, requiring mechanisms to access data stored on different physical nodes.
Why are Merkle proofs used in cross-shard transactions?
Merkle proofs allow a destination shard to verify that a specific transaction occurred on a source shard without downloading the entire history of that shard. They provide a compact, cryptographically secure link between a specific piece of data and the overall state root, enabling efficient and lightweight verification.
Can cross-shard transactions be reversed?
Once a cross-shard transaction is finalized and confirmed by both shards, it cannot be reversed arbitrarily. Like all blockchain transactions, it follows the principle of immutability. However, during the pending phase, if the protocol detects a failure or timeout, it may revert the operation to maintain consistency, effectively canceling the transaction before finalization.
How do fraud proofs protect against malicious shards?
Fraud proofs rely on a challenge period. If a shard posts an invalid state root or receipt, observers have a window of time to submit a proof demonstrating the error. If successful, the invalid block is rejected, and the proposer is penalized. This incentivizes honesty because cheating becomes costly and risky.
Is cross-shard communication slower than regular transactions?
Yes, generally. Regular transactions stay within one shard, requiring only local consensus. Cross-shard transactions involve coordination between shards, proof generation, and verification steps, which adds latency. However, advancements in proof systems are narrowing this gap, aiming for near-instantaneous cross-shard confirmations in future iterations.
Ayodele Emmanuel
September 30, 2026 AT 19:01Yo this is HUGE! 🚀 We need to stop treating shards like isolated islands and start building bridges that actually work. If we get cross-shard comms right, the whole ecosystem explodes with liquidity and speed. Let's gooo!
Michael DeGroat
October 2, 2026 AT 16:33typical crypto bs overcomplicated for no reason. just use one chain like god intended. these sharding schemes are just excuses for bad engineering from people who cant code properly. waste of time.
Ashley Cooke
October 3, 2026 AT 21:44It's important to remember that while the mechanics described are accurate for current research, the user experience layer is often where adoption fails. When explaining Merkle proofs to newcomers, I usually compare them to a receipt in a digital wallet-it proves you bought something without needing to show the entire store's inventory history. This analogy helps bridge the gap between technical verification and intuitive understanding. Also, don't underestimate the psychological barrier of 'pending' states; users hate uncertainty more than they hate fees. Designing UIs that clearly communicate the status of cross-shard locks versus finalizations is crucial for trust.
Furthermore, as we move toward validity proofs, the computational overhead shifts from the network to the prover. This decentralizes the burden but requires robust client-side hardware capabilities. We should be advocating for lightweight clients that can generate these proofs on mobile devices without draining battery life excessively. It’s not just about math; it’s about accessibility and seamless integration into daily financial habits.
sai charan
October 5, 2026 AT 21:37You're missing the point entirely if you think latency is the only issue. The real killer is state bloat during validator rotation. If validators rotate too frequently, the historical state roots become inaccessible or expensive to fetch, breaking the verification chain for older receipts. Most articles gloss over this data availability problem. You can have all the zk-SNARKs in the world, but if the underlying data isn't available when needed, your proof is worthless. Ethereum's DAS is trying to solve this, but it's still experimental and fragile under adversarial conditions. Stop pretending it's solved.
Gary Bryant
October 7, 2026 AT 00:30honestly the atomicity part is where it gets messy because two phase commits introduce liveness issues and if one shard stalls the whole thing hangs which defeats the purpose of parallelization so yeah its complicated
Riya Adhikari
October 8, 2026 AT 04:23Wait, does this mean my NFTs are stuck? 😅 Like, seriously, if I mint on Shard A and want to sell on Shard B, do I lose access until it syncs? That sounds annoying for trading.
Rohit Singh
October 10, 2026 AT 00:06well technically yes but wallets abstract this so you see a pending tx and then boom its there unless the network is congested then you wait lol sarcasm aside its mostly invisible now
Sandy Garg
October 10, 2026 AT 04:26I find the philosophical implication of 'mathematical certainty' over 'trust' quite profound. It suggests a shift from social consensus to pure logical verification. However, one must consider that the code implementing this logic is still written by humans, introducing potential points of failure that mathematics alone cannot fix. The abstraction layers between the user and the cryptographic proof create a distance that may erode the perceived security if bugs arise in the implementation rather than the theory.
Nicoletta Milanesio
October 12, 2026 AT 03:07Love the breakdown! 🌟 The email analogy really helped me visualize it. Can't wait to see how ZK-rollups handle the UX side of things. Fingers crossed for smoother bridging! 🤞✨
Angel Bee
October 13, 2026 AT 06:27This is awesome stuff! Really hope we get to a point where moving money feels as easy as sending a text. Keep up the good work devs! 💪🔥
Daniel Pearson
October 15, 2026 AT 02:40People keep asking why we need this complexity. The answer is simple: scalability. But let's be honest, most users don't care about throughput; they care about safety. If cross-shard communication introduces even a slight risk of double-spending due to race conditions, the entire system loses credibility. We prioritize speed over security at our own peril. Developers need to stop chasing TPS numbers and start ensuring absolute correctness, even if it means slower transactions. Quality over quantity, always.
Douglas Sorocco
October 15, 2026 AT 08:52Actually, the distinction between fraud proofs and validity proofs is far more nuanced than presented here. Fraud proofs rely on an optimistic assumption that requires economic incentives to function correctly, whereas validity proofs provide deterministic finality. However, the article fails to mention the circuit complexity involved in generating zk-SNARKs for arbitrary smart contract execution. It's not just 'high computation cost'; it's a fundamental architectural constraint that limits programmability compared to EVM-equivalent chains. Anyone claiming otherwise hasn't looked closely at the compiler toolchains. 🧐
Joey Eden
October 16, 2026 AT 10:09The jargon here is dense but necessary. I'm curious about the specific networking protocols used for the transmission layer mentioned in step 3. Are we talking libp2p gossipsub optimizations or something proprietary? The efficiency of the relay contracts seems like a bottleneck worth investigating further given the gas costs associated with cross-shard message passing.
Donald Underwood
October 17, 2026 AT 07:09Why is everyone ignoring the centralization risk of relays? If a few entities run the messaging layer, they can censor cross-shard transfers. Who audits these relays? Nobody mentions that. Just assume they are neutral.
Genevieve LeMarchal
October 17, 2026 AT 12:16oh wow this is super helpful!! i was struggling to understand why my tokens took so long to swap across different networks. the merkle tree explanation made it click finally. thanks for sharing this detailed post!!! 🙏💖
Sayantan Bhadury
October 17, 2026 AT 12:24meh. standard info. nothing new.
rose meechan
October 19, 2026 AT 04:09Great overview! 👍 It's reassuring to see the focus on user experience improvements. Keeping the community informed and motivated is key to overcoming these technical hurdles. We've got this! ✨
Katherine Scanlon-Gehn
October 21, 2026 AT 03:47Hold on-does anyone else feel like the 'atomicity' section is oversimplified?? Because in practice, 'atomic' often just means 'eventually consistent' with a timeout, which isn't true atomicity at all!!! And what about the gas spikes when multiple shards try to finalize simultaneously?? That's a huge hidden cost nobody talks about!!! Seriously, read the fine print before believing the hype!!! 🤯⚠️