You send Bitcoin to a friend. The transaction hits the network, gets bundled into a block, and eventually becomes part of an immutable ledger. But what actually stops someone from changing "sent 1 BTC" to "sent 100 BTC" after the fact? It’s not magic, and it’s not just consensus voting. It’s hash functions. These cryptographic algorithms are the glue holding your crypto assets together. They turn any amount of data-whether it’s a single character or a gigabyte of video-into a fixed-length string of characters that acts like a digital fingerprint.
If you’ve ever wondered why changing one tiny detail breaks the entire chain, or how wallets verify your password without storing it, this is where the answer lies. We’re going to look at exactly how these functions work in the wild, moving beyond abstract math to see them protecting your files, securing your logins, and keeping the blockchain honest.
The Digital Fingerprint: How Hashing Works
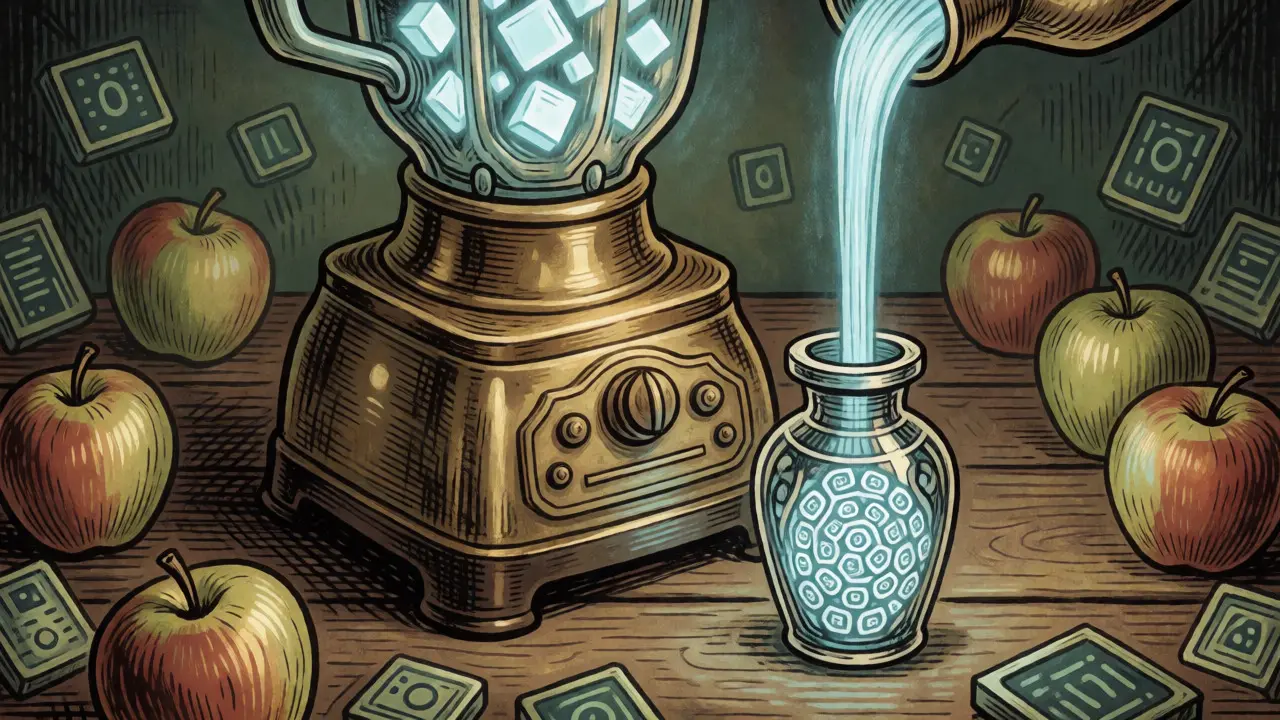
Think of a hash function as a blender for data. You throw in ingredients (data), press the button, and out comes a smoothie (the hash). Here’s the catch: no matter how much fruit you start with, the cup size stays the same. A single apple produces a 256-bit output. A truckload of apples also produces a 256-bit output. This fixed length is crucial because it allows computers to compare huge amounts of data quickly by comparing short strings instead.
But there are two rules that make this useful for security:
- Irreversibility: You can’t un-blend the smoothie. Given the hash output, you cannot calculate the original input. This is why we call them one-way functions.
- The Avalanche Effect: If you change even one bit of the input-say, adding an exclamation mark to a sentence-the resulting hash changes completely. It doesn’t just tweak slightly; it looks like a totally different random string.
This second property is why hash functions are so good at detecting tampering. If a hacker tries to sneak a modification into a file or a transaction, the hash won’t match, and the system instantly flags it.
Bitcoin’s Backbone: Proof-of-Work Mining
The most famous use of hashing is in Bitcoin mining. When miners compete to add a new block to the blockchain, they aren’t solving complex algebra problems. They are guessing numbers until they find one that makes the block’s header hash start with a certain number of zeros.
Bitcoin uses the SHA-256 algorithm. This function takes the block’s data-including the previous block’s hash, timestamps, and transaction lists-and outputs a 64-character hexadecimal string. Miners tweak a value called a "nonce" (a random number used once) inside the block header repeatedly. Each tweak produces a wildly different hash due to the avalanche effect. They keep tweaking until the output meets the network’s difficulty target, such as starting with twenty zeros.
Why does this matter? Because verifying the solution is instant. Once a miner finds the right nonce, other nodes on the network simply plug the data into SHA-256 and check if the output starts with the required zeros. If it does, the block is valid. If a malicious actor tries to change a transaction in that block later, the hash changes, the leading zeros disappear, and the proof-of-work is broken. The entire chain after that point would need to be re-mined, which is computationally expensive and practically impossible to do faster than the rest of the network.
Securing Your Files: Integrity Checks
You don’t need to be a miner to use hashes daily. If you download software, games, or documents, you likely benefit from hashing without realizing it. Developers often publish a checksum-a hash of the file-alongside the download link. This lets you verify that the file you downloaded is exactly the same as the one the developer uploaded.
Let’s say you download a large ISO image for Linux. You run a command like Get-FileHash -Algorithm SHA256 -Path example.iso in PowerShell. The tool spits out a long string of characters. You compare this against the official hash provided on the website. If they match, your file is intact. If they differ, even by one byte, something went wrong during transfer, or worse, a third party modified the file while it was in transit.
| Algorithm | Output Length (Bits) | Hex Characters | Primary Use Case | Status |
|---|---|---|---|---|
| MD5 | 128 | 32 | Checksums, non-critical verification | Vulnerable to collisions |
| SHA-1 | 160 | 40 | Legacy SSL certificates, Git objects | Deprecated for high security |
| SHA-256 | 256 | 64 | Bitcoin, Ethereum, modern security standards | Recommended Standard |
| Keccak-256 | 256 | 64 | Ethereum transactions and addresses | Standard for Ethereum |
Note that MD5 and SHA-1 are still around, but mostly for legacy systems or quick checks where speed matters more than absolute security. For anything involving money or sensitive data, SHA-256 is the current gold standard. Ethereum, interestingly, uses a variant called Keccak-256, which is similar but distinct enough that a SHA-256 hash won’t match a Keccak hash of the same data.
Password Security: Why Sites Don’t Store Your Password
When you sign up for a crypto exchange or a banking app, they rarely store your actual password in their database. Instead, they store the hash of your password. When you log in, the system hashes what you typed and compares it to the stored hash.
Here’s why this protects you: if a hacker breaches the database, they get a list of hashes, not passwords. Because hash functions are one-way, they can’t easily reverse the process to read your password. However, hackers can try "brute forcing" by guessing common passwords, hashing them, and checking for matches. To combat this, developers add a "salt"-a random string added to your password before hashing. This means two users with the same password will have different hashes, making pre-computed attack tables useless.
In Python, a simple implementation looks like this:
import hashlib
password = "MySecretPass123"
hashed_password = hashlib.sha256(password.encode()).hexdigest()
print(hashed_password)
This code turns your readable password into a jumbled string. Even if the site leaks its database, your password remains safe as long as the hashing algorithm is strong and the salt is unique.
Digital Signatures and Wallet Addresses
Your public address in a wallet isn’t just a random string; it’s derived from hashing. In Bitcoin, your public key is hashed twice using SHA-256 and then RIPEMD-160 to create a shorter, manageable address. This saves space and adds a layer of abstraction between your private key and the public world.
Furthermore, every time you sign a transaction, you’re using hashing indirectly. Digital signatures rely on Message Authentication Codes (MACs) and hash functions to prove that you own the private key associated with the address sending the funds. The recipient can verify the signature without ever seeing your private key. If the message content changes-even slightly-the signature verification fails because the hash of the message changes, invalidating the signed digest.
Consider the difference between two nearly identical inputs:
- Input: "StackZero" -> Hash:
a7f...[long string] - Input: "StackZero!" -> Hash:
e361c50cfcd075726095f375520a9b76021ff4ebc06153780ba37d078528be5a
See how different those outputs are? That drastic change ensures that any attempt to alter a signed message is immediately detectable.
Choosing the Right Tool for the Job
Not all hash functions are created equal. As cybersecurity threats evolve, older algorithms fall behind. MD5, once ubiquitous, is now considered broken for security purposes because researchers found ways to create "collisions"-two different inputs producing the same hash. This allowed attackers to forge digital certificates. SHA-1 faced a similar fate, with Google demonstrating practical collision attacks in 2017.
For modern applications, especially in crypto, stick to SHA-256 or newer standards like SHA-3. If you’re building a decentralized application (dApp) on Ethereum, remember that Keccak-256 is the native hasher. Using the wrong one can lead to bugs where your contract expects one format but receives another.
Also, consider performance. Hashing is fast, but doing it millions of times per second (like in mining) requires specialized hardware. This is why ASICs dominate Bitcoin mining-they are optimized specifically for SHA-256 calculations. General-purpose CPUs can handle file verification or login checks easily, but they can’t compete in the mining race.
Frequently Asked Questions
Can two different files have the same hash?
Theoretically, yes. This is called a "collision." Since the number of possible inputs is infinite and the number of possible hash outputs is finite, overlaps must exist. However, for secure algorithms like SHA-256, finding a collision is computationally infeasible with current technology. For weaker algorithms like MD5, collisions can be found relatively easily, which is why MD5 is no longer trusted for security-critical tasks.
Is hashing the same as encryption?
No. Encryption is two-way; you encrypt data with a key and decrypt it with a key to retrieve the original information. Hashing is one-way; you convert data into a hash, but you cannot reverse the hash back to the original data. Encryption hides data; hashing verifies integrity.
Why does Bitcoin use SHA-256 instead of a newer algorithm?
Bitcoin launched in 2009 when SHA-256 was considered state-of-the-art. Changing the core consensus mechanism now would require a hard fork and massive coordination among miners and developers. While newer algorithms exist, SHA-256 remains secure enough for Bitcoin’s needs, and the vast amount of existing mining hardware is built specifically for it.
What happens if I lose my salt in password hashing?
If the salt is lost and wasn't stored alongside the hash, you cannot recover the original password through brute force efficiently because you don't know what string was appended to the password before hashing. Most systems store the salt in plain text next to the hash, so losing the salt usually implies losing the database entry entirely.
Do NFTs use hash functions?
Yes. The metadata of an NFT (which points to the image, description, and traits) is often hashed to ensure it hasn't been altered. Additionally, the token ID and contract address are involved in hashing processes to generate unique identifiers and verify ownership transfers on the blockchain.
liam & the bees
September 8, 2026 AT 21:13Spot on with the blender analogy! It really helps visualize why we can't just reverse a hash. I always tell people starting out in crypto that if you could un-blend the smoothie, your money wouldn't be safe. The avalanche effect is what makes tampering so obvious to the network nodes. Great read for anyone trying to wrap their head around the basics without getting bogged down in heavy math.
Ted Thoroughgood
September 10, 2026 AT 03:32this was super helpful ty
i always get confused between hashing and encryption but this cleared it up real quick
Gabriela Gonzalez
September 11, 2026 AT 04:27Love this breakdown! 🚀 The part about salts saving us from rainbow tables is such a game changer for security. We need more content like this to keep everyone motivated to learn the tech behind the coins! 💪🔒✨
John Martin
September 11, 2026 AT 07:48One thing to add here: while SHA-256 is robust, the hardware race for mining has created some centralization issues. ASICs are great for speed, but they make it harder for hobbyists to participate. Still, the integrity of the ledger remains paramount. 👍
Jess Emmerson
September 13, 2026 AT 06:09Just adding my two cents on the file verification aspect. I use checksums every time I download large datasets for work. It’s peace of mind knowing the data hasn’t been corrupted in transit. Simple, effective, and totally underrated in everyday computing.
Courtney Parker
September 14, 2026 AT 05:05Boring. Everyone already knows this stuff. Why write an article when there are Wikipedia pages? :/
Saket Kulkarni
September 15, 2026 AT 20:24I respectfully disagree with the dismissal above. For those new to the field, this clarity is invaluable. The distinction between irreversibility and collision resistance is subtle but critical. Thank you for presenting these concepts with such formal precision and logical structure.
Eliza Stein-Dodd
September 17, 2026 AT 12:05Actually, Keccak-256 isn't just 'similar' to SHA-256; the padding rule difference is significant for developers implementing low-level protocols. But good intro otherwise. 🧐
Stephen McElreavy
September 17, 2026 AT 15:39The cryptographic agility required to migrate away from legacy systems like MD5 is staggering. Imagine the sheer volume of digital signatures that would become invalid overnight. It’s a testament to the durability of well-designed algorithms that we haven’t faced a catastrophic failure yet. Truly fascinating engineering.
Robert Brabham
September 19, 2026 AT 03:13Sure, hashes stop accidental changes. But do they stop intentional manipulation by powerful entities? If you control the majority of the hash power, you control the truth. The math works, but the politics of mining pools are where the real conspiracy lies. Just saying.
Sonya Kirkwood
September 20, 2026 AT 03:06You are absolutely right to be concerned. The immutability of the ledger is only as strong as the consensus mechanism supporting it. If miners decide to collude, the 'immutable' history becomes mutable for all practical purposes. It is not magic; it is economics wrapped in mathematics.
Charlotte Richardson
September 20, 2026 AT 15:38I appreciate the emphasis on password security. Many users still underestimate the importance of unique salts. It provides a necessary layer of protection against pre-computed attacks, ensuring that even common passwords remain secure within the database context.
Rachel Aldaco
September 21, 2026 AT 22:43Hashing is just society's way of hiding the truth from ourselves. We think we know the input because we see the output, but we never really know what went into the blender. It’s all an illusion of order in a chaotic universe. 😩🌀
Edward Ogunfolaju
September 23, 2026 AT 02:06Stop overcomplicating it! Hashes are fast, they are secure, and they work. That is the bottom line. Don't let the philosophers confuse you with metaphors about chaos. The code runs, the block gets mined, the transaction confirms. Keep building!
Ferdinand Friday
September 24, 2026 AT 13:46When one contemplates the nature of cryptographic primitives, one must acknowledge that the fixed-length output serves as a kind of existential anchor for the infinite possibilities of input data. It is not merely a technical feature but a philosophical statement on determinism versus randomness. The avalanche effect ensures that no fragment of information is lost or diluted; rather, it is transmuted into a wholly new identity, distinct and unrelated to its predecessor, much like how our actions ripple through time, creating consequences that bear little resemblance to the initial cause yet are inextricably linked to it by the laws of physics-or in this case, mathematics. To understand hashing is to understand the fragility of trust in a digital age, where certainty is derived not from memory, but from calculation.